Challenge 1 — Speed
Exploitation of new vulnerabilities across multiple attack surfaces begins in minutes.

For MSPs and MSSPs
Todyl's layered security protects you and your clients across network, identity, endpoint, and cloud through one agent and one portal.

The shift
Capable attacks no longer require capable attackers. Volume and speed have changed more than technique, and you absorb that shift across every environment you protect at once.
Challenge 1 — Speed
Exploitation of new vulnerabilities across multiple attack surfaces begins in minutes.
Challenge 2 — Scale
Attackers can hit hundreds of small and mid-sized organizations at once.
Challenge 3 — Sophistication
Advanced threats and identity theft means attackers log in without a trace.
The requirement
Prevention, detection, and response are three different jobs, and each has to apply across network, identity, endpoint, and cloud. Treating them as separate programs is what leaves the gaps attackers find first.
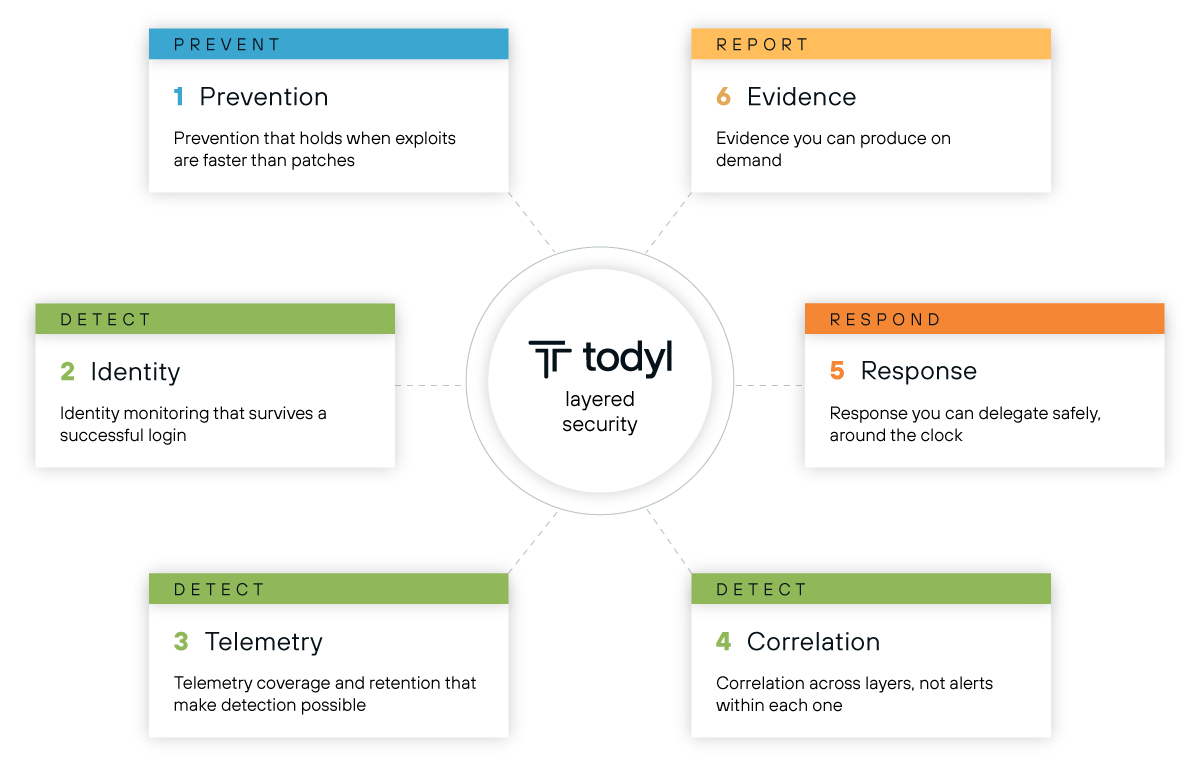
When your security program is siloed, every gap introduces an additional entry point for AI-powered attacks to exploit.
The AI-Ready Assessment asks what a security architect would ask: which techniques your prevention stops, whether your identity telemetry would catch credential abuse, how long you retain detection data, and what you could evidence if an insurer asked tomorrow.
What you get
The platform
Todyl layered security delivers comprehensive advanced threat protection across network, identity, endpoint, and cloud though a single agent and portal.
One agent, one portal, one bill. Let's talk about what your current stack covers, where the gaps sit, and which of them are worth closing first.
Go deeper
Learn more about Todyl layered security and how it can protect you and your clients.
Featured webinar
Forty-five minutes with a Todyl detection engineer and an MSP owner on what changes operationally once patch windows close. Recorded, watch any time.
Watch the recording →Whitepaper
The evaluation criteria behind the assessment, written so you can apply them to a stack you did not build.
Download the whitepaper →From the blog
Speed, scale, and target. Unit 42 research puts threat actors scanning for a new vulnerability within 15 minutes of CVE publication, which effectively closes the window between disclosure and exploitation. One operator can now run credible campaigns against hundreds of organizations at once, because AI automates script generation, reconnaissance, phishing lures, and extortion messaging. That volume lands hardest on SMB and mid-market clients, who are not too small to be targeted so much as cheap to attempt. The techniques are largely familiar. The volume and pace are not.
Because a single control only has to be wrong once, and attackers are now running enough attempts to find the one that is. Layering changes the math in two places. Prevention handles the majority of what arrives, and it is the highest-ROI layer you own: SASE delivers a software defined perimeter with zero trust network access, next-gen firewall, and DNS filtering, while Endpoint Security stops commodity malware before anyone has to investigate it. What gets past prevention meets detection and response built to run at the same speed the attack does. The point of running both is that an attacker has to defeat each stage in turn instead of finding the single gap a point solution left open.
EDR covers the endpoint and RMM covers management, and neither one correlates signals across network, identity, endpoint, and cloud. A failed VPN attempt, an unusual sign-in location, and a new scheduled task look harmless in three separate consoles. Correlating them into one finding requires the layers to share data, which is why Todyl delivers them through the same agent into the same platform rather than as products you integrate yourself.
Nothing that is only looking for a malicious file. Malwareless intrusions and abuse of trusted admin tooling are specifically designed to look like normal administration in any single console, and they end in lateral movement, privilege escalation, and ransomware within minutes. What separates that from an admin doing their job is behavior over time and across layers, so detection has to profile behavior against telemetry from the network, identity, endpoint, and cloud together. That correlation is what tells a suspicious action apart from an obviously malicious one, and it is why the visibility layer is not optional groundwork for the detection layer.
No. Deploy the full platform, or start with the single module a client needs today and add the rest with a toggle in the UI. Most partners begin with the layer their clients are weakest on and expand from there, and because every module runs through the same agent, adding one is a licensing decision rather than another deployment project for your techs.
Yes. Janus SIEM Search & Analysis uses natural language query building, so a tier-1 tech can investigate without first learning a query syntax. Once the investigation is complete, Janus returns key observations, notable findings, expert insights, and suggestions for additional queries and related threat hunts. For the hours you do not staff, MXDR analysts monitor, investigate, and respond around the clock.
Either. Todyl MXDR is a full 24x7 expert managed detection and response service that can deliver after hours solutions with or without the need for MSPs to staff after hours. Escalation and response authority can be scoped for each tenant based on the coverage they need and the level of hands-on support required for appropriate escalation.
Start with what the cheaper option leaves out. Low-cost tools cut corners on visibility, coverage, and detection and response, and when one of them fails, the cost and the responsibility land on you and your client rather than on the vendor. Multi-stage extortion is more profitable for the attacker and more expensive for the target than the ransomware of a few years ago, so the downside has grown while the tooling underneath many stacks has not. A layered platform also lowers your operating overhead, because your techs learn one portal instead of six, and it gives the client posture they can use: cleaner cyber insurance renewals, simpler regulatory compliance, and evidence of security capability when an enterprise customer audits their supply chain.
Ten questions, roughly five minutes, results on screen. You get scored one to four in each of six domains: attack surface, identity and access, endpoint defense, detection and visibility, response readiness, and AI governance. Below the scores, the assessment reads the pattern back to you and names specific moves per domain, such as zero trust network access and least-privilege controls for attack surface, or behavioral analytics and correlated SIEM alerting for detection. Detection and visibility and response readiness are the most common weak points, and that is the useful part of the result. If your techs are correlating alerts by hand or response depends on manual escalation, those are the gaps AI-accelerated attacks are built to exploit first, and another point product does not close them for a stack whose layers have no way to share data.