Secure AI.
Inside and out
Todyl brings visibility and control to AI applications and agents, backed by AI-powered protection and 24x7 security experts, all through one unified platform.
One platform. Two sides of AI security.
AI is changing how businesses operate and how attackers target them.
Your clients need to know what the AI already inside their business is doing.
Most security strategies cover the first part. Todyl protects against both.
AI Joined the Team. You call the shots.
Know which AI app and agents are in use, define what's allowed, and track activity. Bring visibility, control, and accountability to AI adoption.
The attackers have AI. So do we.
Attackers use AI to sharpen their scams and accelerate attacks. Todyl pairs AI-speed detection with 24x7 human experts, so threats get stopped faster and handled right.
Four Pillars. One Strategy. One Platform.
Point tools a bit here and a bit there leaving you with the gaps and complexity. Todyl brings visibility, control, protection, and proof together in one. layered security strategy.

Turn the lights on, inside and out
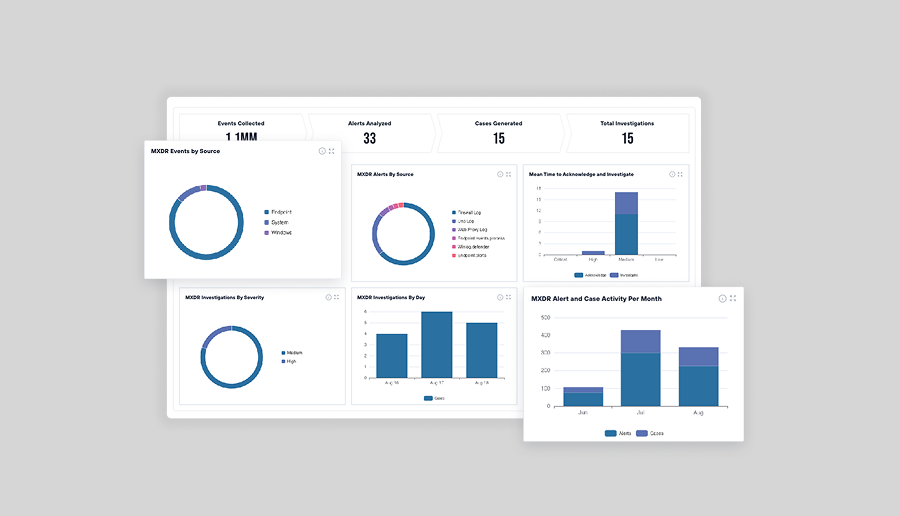
Bad actors love dark corners. See what’s happening across identity, endpoint, network, email, and cloud, including AI activity. Connect the signals, understand the context, and get answers without digging through disconnected tools.
- See which AI tools are in use.
- Bring related alerts and evidence into one clear picture.
- Get answers in plain language with Todyl’s Janus AI.
- Flexible data retention for investigations and audits.
Shrink the target. Set the rules.
It's hard to hit what you can't find. Give AI clear boundaries and attackers fewer ways in. Govern access, reduce exposure.
- Allow approved AI tools. Restrict the rest.
- Reduce public exposure and control who connects.
- Give attackers fewer ways in.
- Stop lateral movement with micro segmentation.
- Phishing and BEC caught before the inbox.
Hackers work nights. So do we.
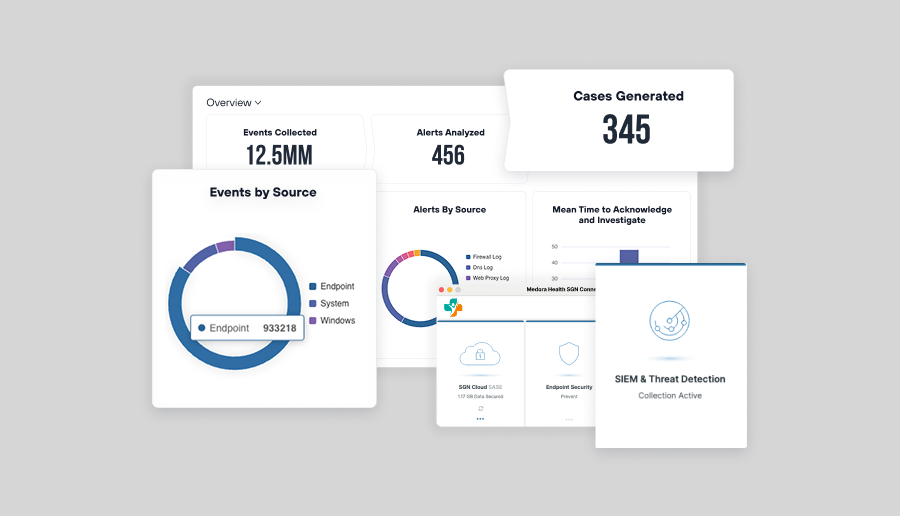
Spot and contain threats at machine speed, with automated response and 24x7 human experts who never hit snooze.
- Behavioral detection and AI-powered investigation catch what signatures miss.
- GenAI detections on every device
- Automated response actions to contain compromised devices and accounts.
- 24x7 SOC with experts-led response.
Receipts at the ready
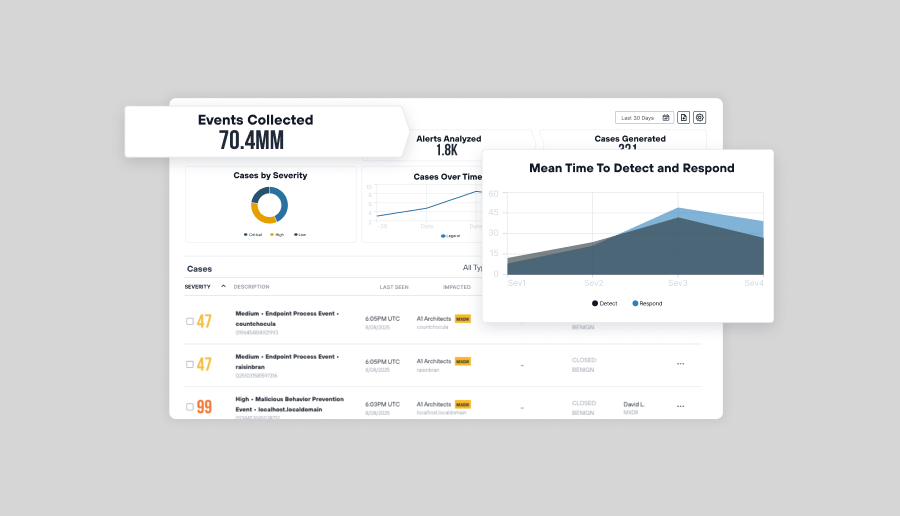
"Trust me" isn't evidence. Show auditors, insurers, and boards that controls are in place and working. Connect AI activity, security controls, and response outcomes to demonstrate oversight and accountability.
- Controls mapped across CIS, NIST CSF, PCI DSS, NIST 800-171, and HIPAA.
- Ongoing collection and retention of security evidence.
- AI activity records alongside broader security events.
- Response times reported, including MTTD and MTTR.
Good Questions. Straight Answers.
What is AI security?
AI security protects businesses as AI changes how they work and how attackers target them. Todyl combines secure AI adoption, AI--powered defense, and protection against modern threats in one unified platform.
What's the difference between external and internal AI security?
Ask who is using the AI. If it's an attacker, that's external: the job is to stop the attack. If. it's the business's own people or tools, that's internal: the job is to see it, set limits, and catch misuse.
What is shadow AI?
Shadow AI is AI apps, browser extentions, and agents used without approval. The risks include sensitive data pasted into prompts, AI used outside policy, and AI tools reaching places they shouldn't.
How does AI change cyberattacks?
Finding weak spots, phishing, stolen-password attacks, and moving through a network all happen faster, at larger scale, and more convincingly.
Are Todyl's AI threat detections an add-on?
No AI threat prevention is on for every package. Todyl's 22 GenAI detections are live for every tenant, with nothing to switch on and no upgrade to buy.
How does Todyl help MSPs prove security to auditors and insurers?
Todyl maps controls once across frameworks including CIS, NIST CSF, PCI DSS, NIST 800-171, and HIPAA, retains the evidence over time, and reports repsonse metrics such as MTTD and MTTR. AI events sit in the same record as every other control.
Testimonials
"It was clear that Todyl’s MXDR was truly looking out for us 24/7. When I got the call from their detection engineers on a Sunday, I asked them to jump in and help us and they agreed right away."
"End users have shared that they love that they log in to their PC and it just works, whether they are in one of the office locations, at home, or traveling."
“Todyl has been invaluable to our growth over the past year. The team is more than just another vendor, they’re a business partner we can turn to for crucial cybersecurity knowledge and support whenever we need it.”
“Before Todyl, we were using about 8 tools per machine, which was a hassle to image and onboard. Now, we just use Todyl and our RMM, and have cut our onboarding time down to less than an hour. It’s just as easy for offboarding.”
"We rely on their expertise, and we can always turn to them with any questions. Working with Todyl feels like a true partnership because they make time for us, listen, and implement our feedback."
"We know what regulations our clients are up against. We use Todyl to head off potential issues before they become pain points."
"Switching to Todyl helped us achieve every initial goal and more, With Todyl, my team can deliver better security through a single-pane-of-glass with robust reporting that we didn’t have with multiple vendors."
"The visibility from SIEM and the support from Todyl’s MXDR team were extremely helpful during a stressful time."
See AI security from both sides
Attackers are using AI. So are your clients' teams. Todyl keeps an eye on both. On one platform, with the evidence to back it up.