Stop the email attacks your existing filters miss
Todyl Email Security works alongside Microsoft 365 and Google Workspace to catch advanced phishing and BEC that built-in filters let through, and removes them before anyone clicks.
$3B
in reported BEC losses 2025 (FBI IC3 2025 Internet Crime Report)
191,561
phishing and spoofing complaints (FBI IC3 2025 Internet Crime Report)
62%
of breaches involved the human element. (Verizon 2026 Data Breach Investigations Report)
Identify malicious emails that look normal
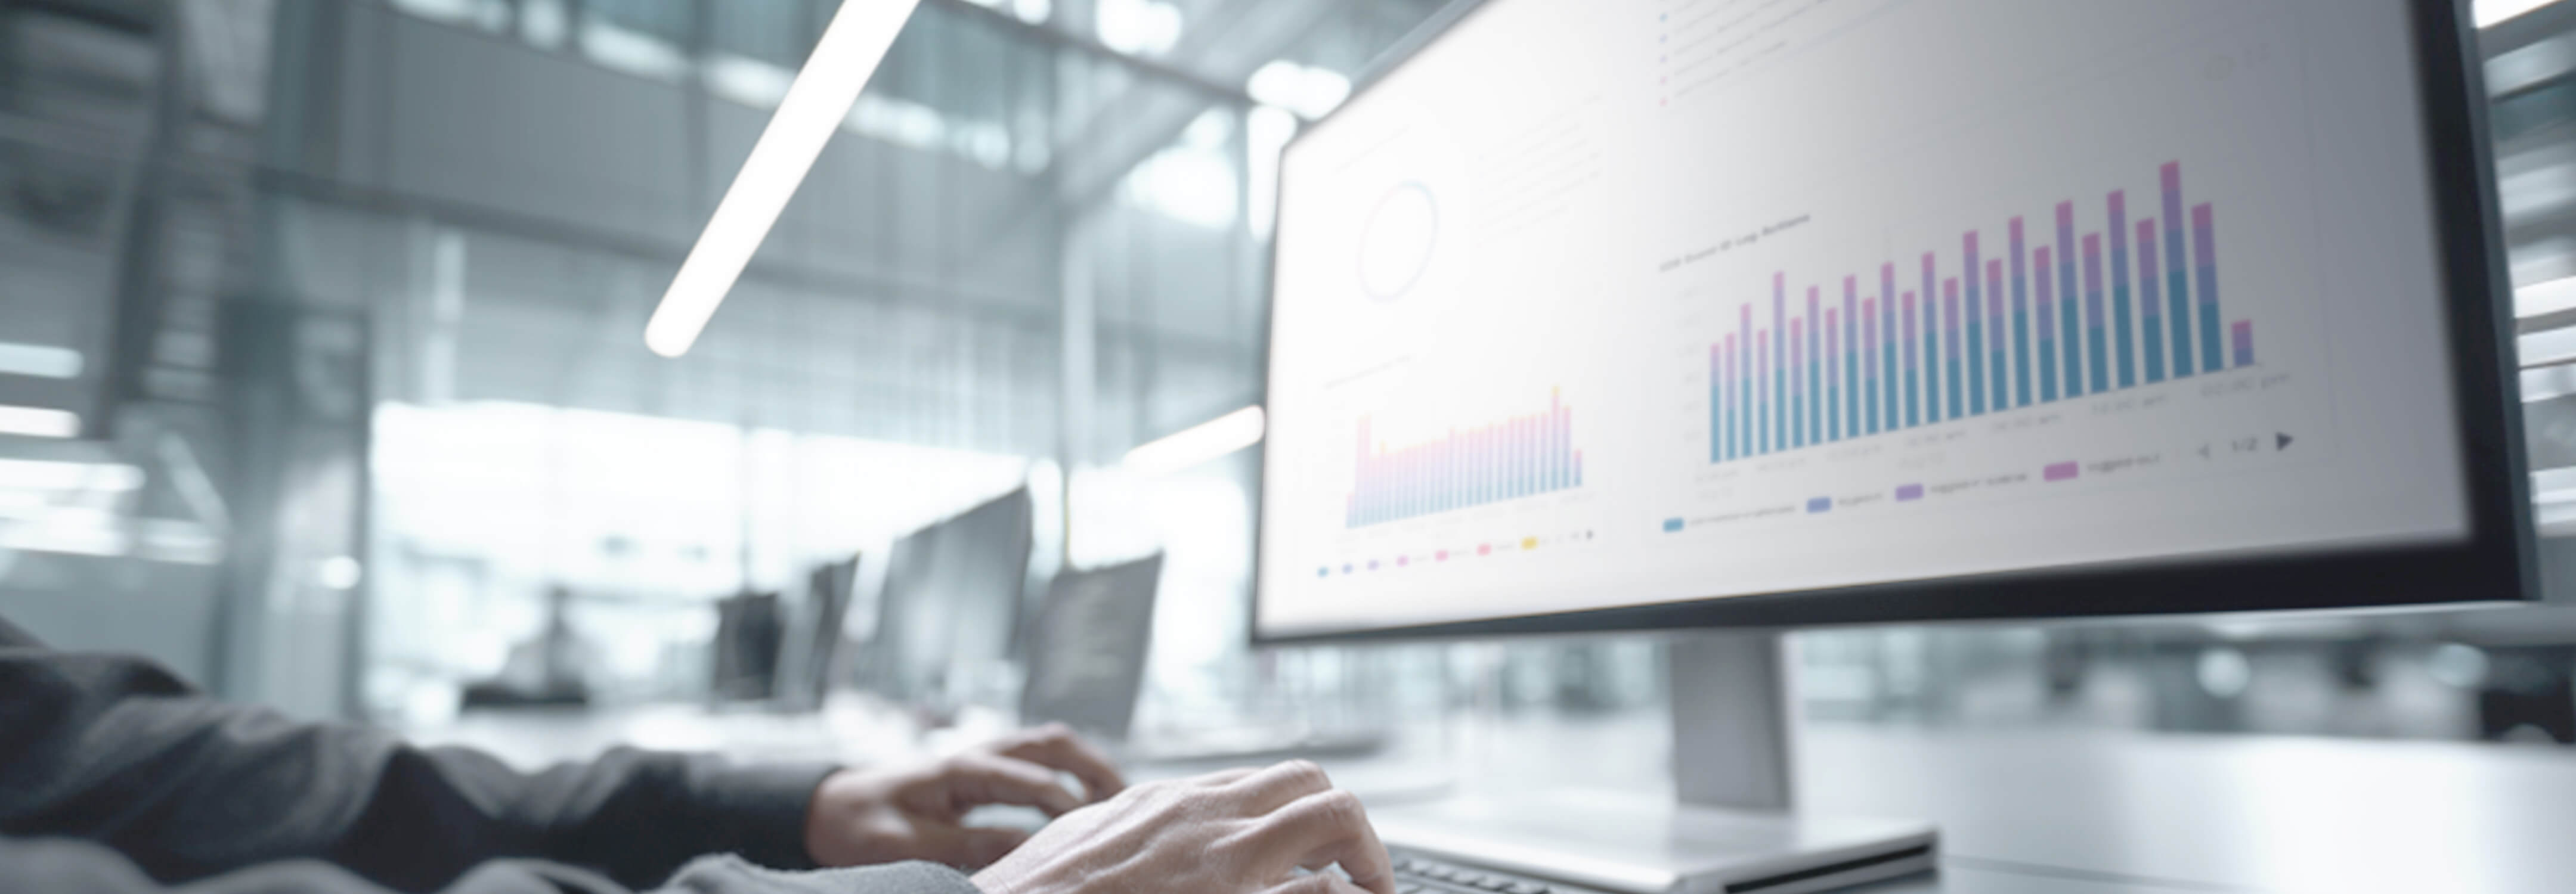
A sophisticated fake wire request or a spoofed invoice often has no bad link or attachment, so filters let it through. Todyl Email Security learns how each employee normally communicates and flags messages that don’t fit.
Works with what you have
Email Security connects easily to Microsoft 365 and Google Workspace by API. Setup takes minutes, with no MX record changes.
Less work for you
Employee reports are investigated automatically and expert analysts review the unclear cases. Your help desk doesn’t get a ticket.
Headline goes here
Paragraph statement goes here

Stop fraud before money moves
Catch the phishing and BEC emails that look like normal business, before an employee pays a fake invoice or hands over a password.
- Behavioral analysis for each mailbox
- Catches phishing, BEC, impersonation, and malicious attachments
- Optional warning banners in suspicious emails
Spend less time on phishing response
One detection or employee report removes the threat from every inbox that received it. You stop searching mailbox by mailbox.
- Automatic quarantine
- All copies removed in one action
- One-click reporting in Outlook and Gmail
Turn employee reports into fast answers
Employees can flag a suspicious email in one click. Each report is investigated automatically, and expert analysts review the unclear cases.
- One-click reporting in Outlook and Gmail
- Optional warning banners in suspicious emails
- Analyst reviews train the model for accuracy
Show clients it’s working
Audit logs record every detection and response action, giving you the records auditors and cyber insurers ask for.
- Audit logs for every client
- Per-client management from one console
Built for how email works today
Traditional email gateways were designed to filter mail before it reached an on-premises server. Todyl Email Security works inside Microsoft 365 and Google Workspace, where your mail already lives.
Traditional email gateway
Todyl Email Security
Stop the email attacks your existing filters miss
Todyl Email Security works alongside Microsoft 365 and Google Workspace to catch advanced phishing and BEC that built-in filters let through, and removes them before anyone clicks.
Good Questions. Straight Answers.
What is business email compromise (BEC)?
BEC is when an attacker impersonates or takes over a trusted account, like a vendor or coworker, to request a payment or steal credentials. These emails usually have no malicious link or file, so standard filters miss them.
Does this replace Microsoft 365 or Google Workspace filtering?
No, Microsoft and Google keep filtering mail, and Todyl catches the attacks they miss.
How is this different from a secure email gateway?
A gateway sits in front of your mail server and checks messages once using known signatures. Todyl connects by API, learns normal behavior for each mailbox, scans internal email, and keeps checking messages after delivery.
What happens when an employee reports an email?
The report is investigated automatically. If the email is malicious, it is removed from every mailbox that received it.
How does Email Security work with the rest of Todyl?
If an attacker still gets credentials, Todyl ITDR detects the account takeover and the 24x7 MXDR team responds.
Testimonials

"It was clear that Todyl’s MXDR was truly looking out for us 24/7. When I got the call from their detection engineers on a Sunday, I asked them to jump in and help us and they agreed right away."

"End users have shared that they love that they log in to their PC and it just works, whether they are in one of the office locations, at home, or traveling."

“Todyl has been invaluable to our growth over the past year. The team is more than just another vendor, they’re a business partner we can turn to for crucial cybersecurity knowledge and support whenever we need it.”

“Before Todyl, we were using about 8 tools per machine, which was a hassle to image and onboard. Now, we just use Todyl and our RMM, and have cut our onboarding time down to less than an hour. It’s just as easy for offboarding.”

"We rely on their expertise, and we can always turn to them with any questions. Working with Todyl feels like a true partnership because they make time for us, listen, and implement our feedback."

"We know what regulations our clients are up against. We use Todyl to head off potential issues before they become pain points."

"Switching to Todyl helped us achieve every initial goal and more, With Todyl, my team can deliver better security through a single-pane-of-glass with robust reporting that we didn’t have with multiple vendors."

"The visibility from SIEM and the support from Todyl’s MXDR team were extremely helpful during a stressful time."
Know what you're saying yes to
Your clients are going to adopt ai either way. Todyl lets you say yes to it, with the visibility, the controls, and the evidence to show it is governed.