Hackers got an upgrade.
So can you.
AI may not have reinvented the threat playbook. But it’s certainly upped the pace. Todyl helps you see across every plane, reduce your attack surface, and contain threats at the attackers’ speed.
32%
of intrusions initially caused by exploits. The #1 infection vector for six years running.
29%
of known vulnerabilities are exploited on or before the date of CVE publication.
50x
increase in potential profitability when attackers use AI.
Same Old Tricks. Now on Steroids.
Attackers use AI to find exploits faster than patch cycles, write phishing that sounds like your favorite colleague, and walk through networks like they own the place. We keep you one step ahead.

Already on. No added complexity.
AI threat prevention is on for every package. No new SKU, no awkward upsell conversation. Just better protection, faster containment, and the evidence to show your clients it worked.
Small team. Big-time defense.
Running security in-house? Get one platform and 24x7 expertise in your corner without stitching tools together or pouring money into staffing a SOC.
Layer Up.
Meet AI-accelerated attacks at every step, from the first step in the attack chain to the reporting that follows. With a layered strategy built on visibility, control, protection, and proof.

Bad actors hate bright lights
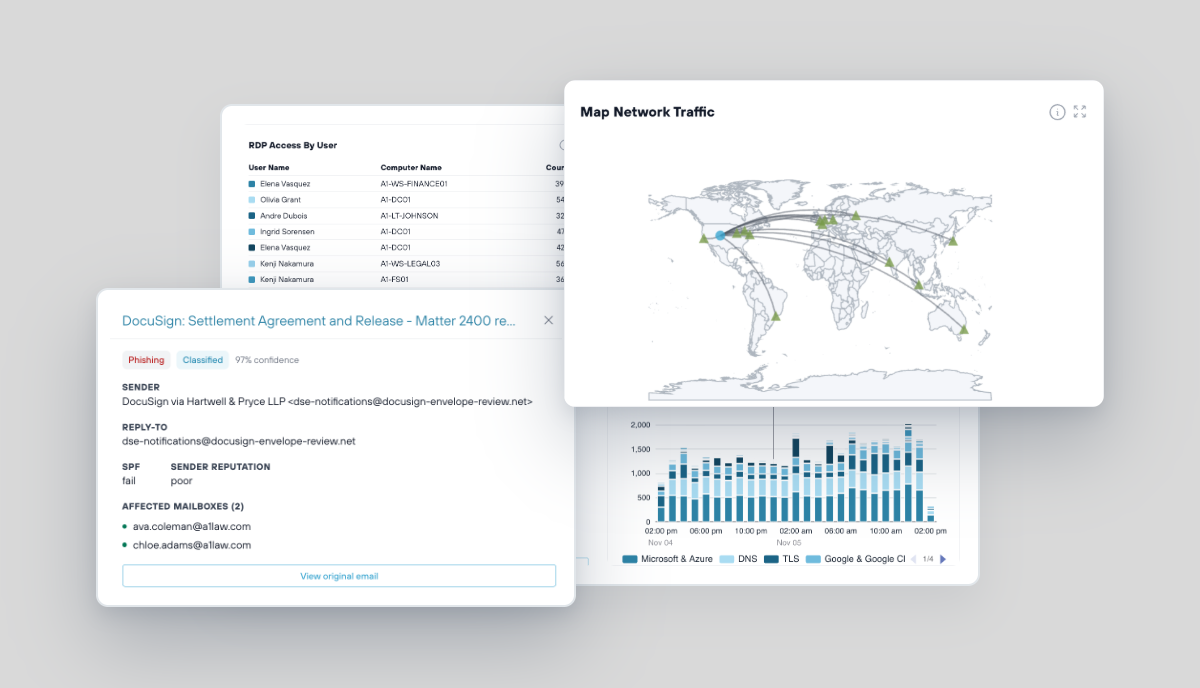
Attackers log in rather than break in, hiding in the gaps between your logs. Bring every plane into one view.
- Endpoint, identity, network, and cloud in one schema
- Full data retention to rebuild the attack
- Key activities collected and analyzed by default
- Simple, natural language forensics with Janus SIEM Search
Give attackers a smaller target
The cheapest incident is the one that never starts. Limit what AI-driven attacks can find and access.
- SASE removes clients from an attacker’s line of sight
- Access to protected resources blocked, even with valid credentials
- LAN Zero Trust microsegmentation stops lateral movement
- Email Security and ITDR defend against phishing, BEC and account takeover
See the hidden threats
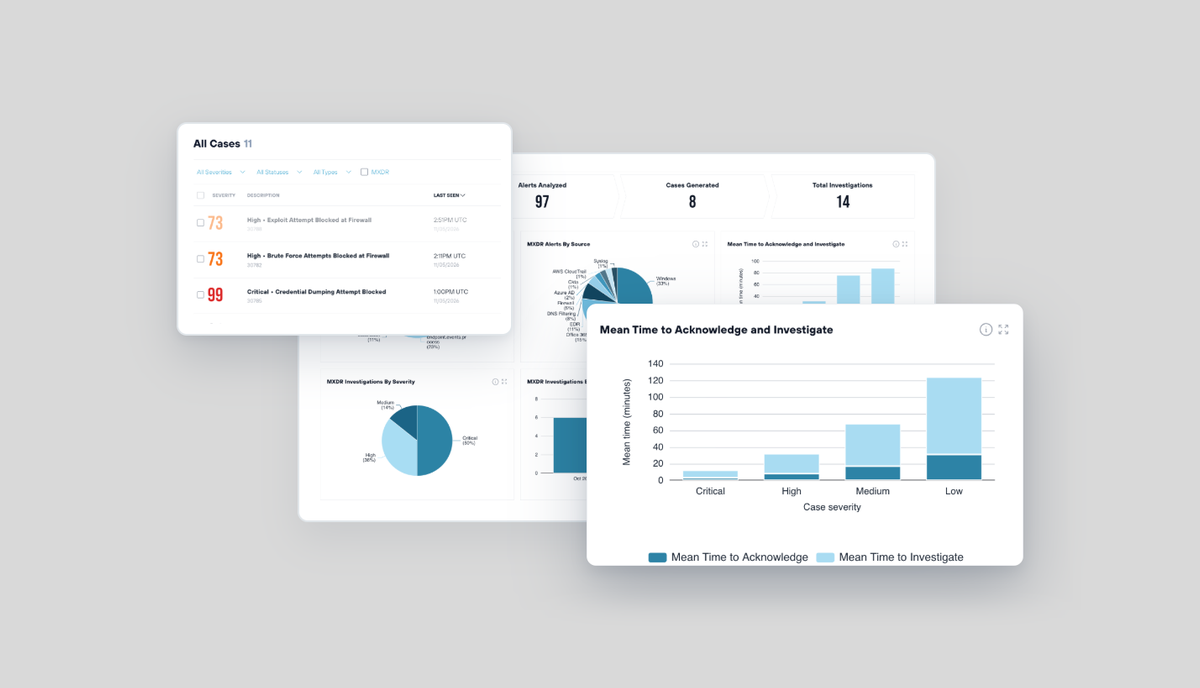
When AI-driven activity looks like normal admin work, signature-based tools get fooled. Respond at machine speed, with human experts confirming every call.
- Behavioral profiles built across identity, endpoint, network and cloud
- 24x7 MXDR and ITDR with a human in the loop
- SOAR playbooks isolate hosts, disable accounts and revoke tokens
- GenAI detections to protect against AI-powered threats
Posture you can prove
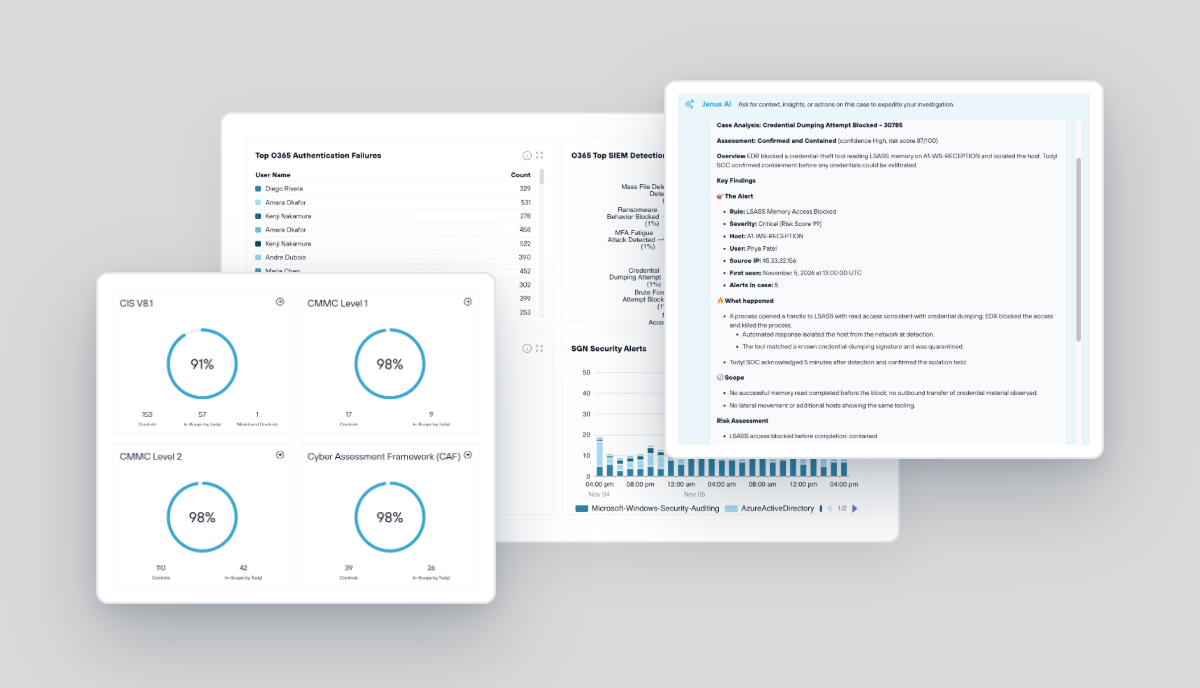
Auditors, insurers, and boards don’t grade on vibes and promises. Turn the telemetry that drives detection into evidence for your clients.
- Controls mapped once across CIS, NIST CSF, PCI DSS, NIST 800-171 and HIPAA
- Continuous evidence replaces one-day audit screenshots
- Retained data that turns an audit into a query
- MTTD, MTTR and time to contain reports
Good Questions. Straight Answers.
What are AI-powered attacks?
AI-powered attacks are often familiar attacks, like phishing, stolen-password logins, vulnerability scanning, and lateral movement. However, they run faster, at larger scale, and more convincingly using AI. Some are fully autonomous, others are accelerated by AI at each step.
How do you defend against AI-powered attacks?
With a layered strategy across four jobs: see the whole environment, reduce the attack surface, detect and contain at the attacker’s speed, and prove the posture held. Todyl delivers all four on one platform.
Can Todyl stop an attacker who has valid credentials?
Todyl’s SASE blocks access to protected resources even when credentials or tokens are stolen. Microsegmentation with Todyl’s LAN Zero Trust stops lateral movement and Identity Threat Detection and Response (ITDR) detects compromised identities and contains the threat.
Does Todyl use AI to detect threats?
Yes. Todyl uses AI to detect and analyze threats at machine speed, with human analysts in the loop to confirm each call. AI is also built into SIEM search and case analysis through Janus.
Who responds when an alert fires overnight?
Todyl’s MXDR team works 24x7, and SOAR playbooks can isolate hosts, disable accounts and revoke tokens automatically.
How does Todyl help with cyber insurance and audits?
Todyl maps controls once across frameworks including CIS, NIST CSF, PCI DSS, NIST 800-171 and HIPAA, retains evidence over time, and reports MTTD and MTTR. So you can prove that you have a program in place and how the relevant controls operated.
Testimonials

"It was clear that Todyl’s MXDR was truly looking out for us 24/7. When I got the call from their detection engineers on a Sunday, I asked them to jump in and help us and they agreed right away."

"End users have shared that they love that they log in to their PC and it just works, whether they are in one of the office locations, at home, or traveling."

“Todyl has been invaluable to our growth over the past year. The team is more than just another vendor, they’re a business partner we can turn to for crucial cybersecurity knowledge and support whenever we need it.”

“Before Todyl, we were using about 8 tools per machine, which was a hassle to image and onboard. Now, we just use Todyl and our RMM, and have cut our onboarding time down to less than an hour. It’s just as easy for offboarding.”

"We rely on their expertise, and we can always turn to them with any questions. Working with Todyl feels like a true partnership because they make time for us, listen, and implement our feedback."

"We know what regulations our clients are up against. We use Todyl to head off potential issues before they become pain points."

"Switching to Todyl helped us achieve every initial goal and more, With Todyl, my team can deliver better security through a single-pane-of-glass with robust reporting that we didn’t have with multiple vendors."

"The visibility from SIEM and the support from Todyl’s MXDR team were extremely helpful during a stressful time."
An AI for an AI
AI shortened the attack. Todyl shortens the response, and gives you the evidence to show clients, insurers, and auditors that it worked.